
CRM data governance is the set of policies, owners, and controls that keep customer records accurate, secure, and usable across sales, marketing, and support. The single target that matters most: a duplicate rate under 2% and a required-field fill rate above 90%, the two KPI thresholds practitioners point to most often. Everything else in this framework exists to meet those two numbers and keep them there.
TL;DR:
- Achieving a duplicate rate below 2% and a fill rate above 90% requires enforcement at data entry and regular audits of required fields.
- Building a simple, clear data governance framework includes a one-page charter, a living data dictionary, and clearly assigned ownership roles.
- Activating native duplicate detection and validation rules in CRM systems offers quick wins and reduces manual cleanup efforts.
- Governance must be an ongoing, iterative process with dashboards tracking duplicate and fill rates, not a one-time policy document.
- Proper controls for privacy and security, like encryption and audit logs, are critical for compliance and operational trust in customer data.
Table of Contents
- Why CRM Data Governance Matters for Revenue and Trust
- What Actually Sinks a CRM Governance Program
- Building the Governance Framework: Standards, Owners, and Controls
- The 30/90/180-Day Governance Rollout
- Privacy, Compliance, and Security Controls to Build In
- How Sales-phoenix Applies Governance to Revenue Recovery
- What Governance Looks Like Once AI Enters the CRM
- Where Sales-phoenix Fits Into Your Governance Rollout
- Sources
- FAQ
Why CRM Data Governance Matters for Revenue and Trust
A CRM full of duplicate contacts, blank fields, and stale ownership records doesn't just look messy. It actively distorts the numbers leadership uses to run the business.
Forecasts built on incomplete pipeline data skew in both directions: reps inflate close probabilities to compensate for missing context, or deals fall through the cracks because nobody owns the follow-up. Marketing sends the same nurture sequence to three versions of the same contact because dedupe never ran. Customer success misses a renewal risk because the account record never got updated after a support escalation.
The costs show up in specific, avoidable ways:
- Wasted rep time chasing contacts who already got called by a teammate that morning.
- Skewed forecasts when territory or stage data is inconsistent across the team.
- Duplicate outreach that annoys prospects and damages sender reputation.
- Executive distrust in dashboards, which quietly kills adoption of the tools built to run the business.
That last point matters more than most teams realize. Once a VP catches one bad number on a dashboard, they stop trusting all of them, and they go back to running the business on gut feel and spreadsheets. Governance isn't a data hygiene exercise. It's what keeps the numbers credible enough for people to act on them.
What Actually Sinks a CRM Governance Program
Most governance efforts don't fail because nobody cared. They fail because the program was built to look good in a slide deck, not to survive contact with a busy sales team.
- Governance as a document, not an enforcement system. A 12-page PDF titled "Data Standards" that sits in a shared drive changes nothing. Standards only work when they're enforced at the point of data entry, not described after the fact.
- Too many required fields. Make 15 fields mandatory to save a record, and reps will type "N/A" or a single space just to get past the form. Governance dies here more often than anywhere else.
- No clear steward, so standards decay. Without someone accountable for monitoring quality, picklists drift, naming conventions fragment, and every team invents its own shortcuts within two quarters.
- No visible metrics, so there's no accountability. If nobody can see the duplicate rate or fill rate on a dashboard, nobody feels pressure to fix it.
Pro Tip: Before you write a single new rule, audit which required fields reps are already faking with junk values. That list tells you exactly where your current governance is already broken.
Enforcement works best across three layers at once, technical automation, process workflow, and cultural accountability, rather than leaning on any single one, according to HubSpot's governance guidance.
Building the Governance Framework: Standards, Owners, and Controls
A working governance framework rests on four artifacts you can actually point to, not a vague commitment to "better data."
Start with a one-page charter. This isn't a policy manual. It's a single page that states which fields matter, why, and how they connect to pipeline or revenue goals. A charter that says "accurate close-date fields improve forecast accuracy" gets executive buy-in faster than a 40-slide governance proposal ever will, and that link between data quality and revenue outcomes is what wins the sponsorship Prospeo's practitioner guide points to as the deciding factor.
Build a living data dictionary. Every field needs a defined format, a picklist where applicable, and a clear required-versus-optional status. "Industry" as a free-text field guarantees forty spellings of "healthcare." A locked picklist guarantees one.
Define ownership at three levels:
- RevOps or system owners who control schema, integrations, and platform-wide rules.
- Record owners, typically the rep or account manager, responsible for the accuracy of their assigned accounts.
- Rotating data stewards, a functional responsibility inside RevOps rather than a separate headcount line, who monitor quality dashboards and intervene on emerging trends.
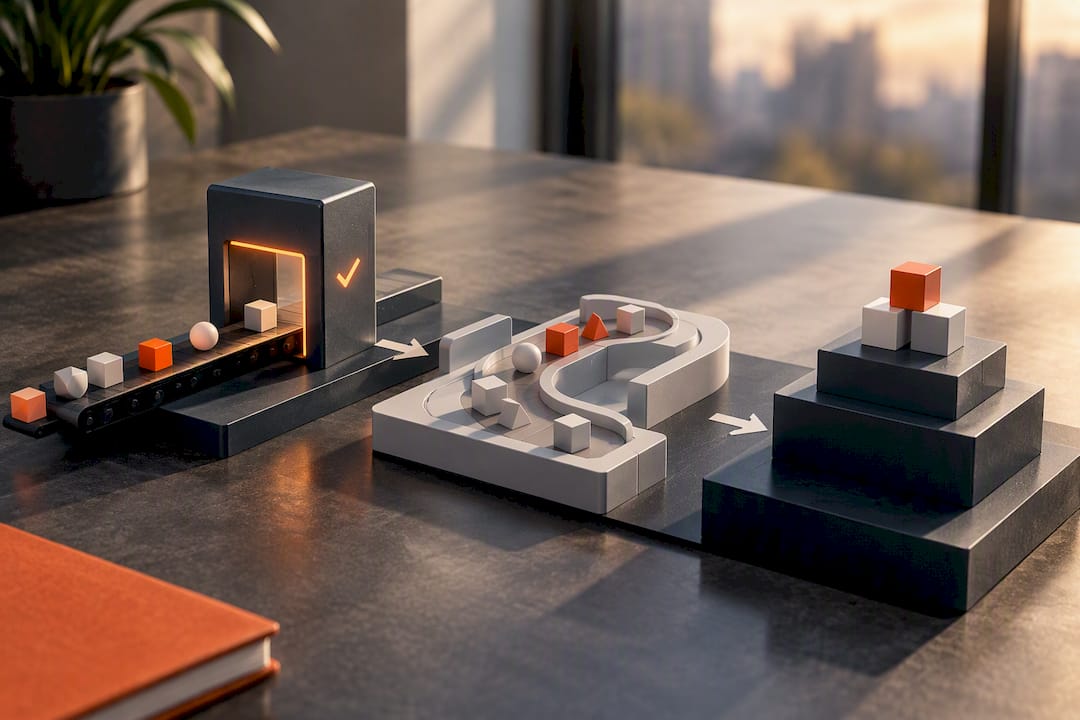
Layer enforcement at the point of entry. Validation rules catch malformed emails and phone numbers before they save. Duplicate-detection logic flags matches before a second record gets created. Enrichment tools fill gaps automatically for firmographic data. Human-in-the-loop approval catches the edge cases automation misses, like a merge that would wipe out custom notes.
Catalog your technology controls. List every validation rule, every role-based or attribute-based access control, every field with masking applied, and every audit log you can pull on demand. This inventory becomes your evidence trail when a client or regulator asks how you protect their data, and it pairs directly with the DPA and subprocessor terms you should already be collecting from every vendor touching that data. A data catalog and master data management approach gives this inventory a searchable home instead of a scattered set of spreadsheets.
The 30/90/180-Day Governance Rollout
Governance programs stall when the first milestone is six months away. Fix that by front-loading wins your team can see within a week.
Three quick wins to run this week:
- Audit required fields. Pull a report of every mandatory field and how often it contains junk values like "N/A" or a placeholder character. Cut or fix the worst offenders immediately.
- Turn on duplicate alerts. Most CRMs have native or low-cost duplicate-detection features sitting unused. Activate them before you build anything custom.
- Sanity-check your picklists. Open every dropdown field and merge near-duplicate values ("Health Care," "Healthcare," "Medical") into one standard entry.
The 30/90/180-day milestones:
At 30 days, aim to cut your duplicate rate toward the 5% mark, the threshold below which practitioners recommend fixing dedupe before investing in enrichment.
Small, repeatable controls, entry-point validation, duplicate alerts, weekly enrichment passes, tend to outperform large annual cleanup projects, since incremental fixes compound while big-bang cleanups decay again within months.
Build dashboards by team and by individual rep, and make governance metrics a standing line item in weekly pipeline reviews, not an annual audit nobody remembers. When a rep or team stays non-compliant after training and a documented warning, escalate to their manager with the specific metric attached, not a general complaint about "data quality."
Privacy, Compliance, and Security Controls to Build In
Governance and compliance overlap heavily, but they aren't identical. Compliance sets the legal floor; governance is how you operationally clear that floor every day.
Your CRM needs functioning export and deletion workflows to handle data subject access requests (DSARs) without a week of manual searching, plus a verification step to confirm the requester's identity before releasing anything. If your DSAR process is still manual and slow, freeze new personal-data field additions until automation catches up. Compliance debt compounds faster than data debt.
At a high level, GDPR recognizes six lawful bases for processing personal data: consent, contract performance, legal obligation, vital interests, public interest, and legitimate interest. Knowing which basis applies to which CRM field determines how long you can retain it and what happens when someone withdraws consent.
Security controls worth requiring across every system touching customer data:
- AES-256 encryption at rest
- Multi-factor authentication for all user accounts
- Full audit logging of access and changes
- Least-privilege access by default
- Signed DPA terms with subprocessor transparency from every vendor
Vendor Data Processing Agreements typically spell out controller and processor roles, subprocessor lists, and DSAR assistance terms, and customers can usually object to new subprocessors within a notification window if they request that clause up front, as HubSpot's own DPA demonstrates.
Jurisdiction-specific rules vary enough that a compliance lawyer should review your final policy before it ships.
How Sales-phoenix Applies Governance to Revenue Recovery
Governance work feeds directly into the Phoenix Growth Framework™: clean, well-owned CRM data is what lets the framework locate leaked revenue instead of guessing at it.
In practice, that means installing executive dashboards that make duplicate rate and fill rate visible weekly, assigning a steward cadence inside RevOps rather than adding headcount, and running database reactivation flows that recover value from accounts governance previously let go stale.
What Governance Looks Like Once AI Enters the CRM
Governance built for a spreadsheet-era CRM breaks the moment AI enrichment, predictive scoring, and cross-system integrations enter the picture, because each one introduces a new place for bad data to multiply unnoticed. The frameworks that hold up treat governance as a living system with quarterly review cycles, not a policy you write once and file away. Measure it, watch the trend lines, and adjust. A governance program that isn't iterating is already decaying.
— Hunter
Where Sales-phoenix Fits Into Your Governance Rollout
Building the charter, dictionary, and enforcement layers described above takes real operational bandwidth, and most RevOps teams are already stretched across a dozen other priorities. Sales-phoenix exists for exactly that gap: instead of hiring a full governance team or hoping a generic consultant understands your CRM, you get a partner that ties data controls directly to the revenue numbers your executives already watch.
If your CRM has ownership gaps, no visible metrics, or a duplicate rate nobody has measured in over a year, that's the moment to bring in outside help. Some specialized services focus on reviving stale records, installing steward workflows, and building dashboards to make data quality visible to leadership. Some advisory services offer operational leadership support without requiring a full executive hire.
Start with a look at the full services lineup to see which engagement fits your current gap, and take that as your first concrete step toward a governance program that actually holds.
Sources
The KPI targets and rollout sequence draw on Prospeo's practitioner guide. Governance-versus-management distinctions come from Alation's data management framework. Compliance mapping references IAPP's GDPR lawful-basis refresher and HubSpot's published DPA.
- Refresher: The GDPR’s six legal bases for data processing | IAPP
- CRM Data Governance: A Practitioner's Guide (2026) | Prospeo
FAQ
What Is CRM Data Governance?
CRM data governance is the combination of policies, ownership structures, and enforcement controls that keep customer records accurate, secure, and consistently usable across teams. It differs from data management, which is the day-to-day execution of those policies, because governance sets the rules while management runs them.
What Are the Top CRM Data Governance Tools?
Most CRM platforms include native duplicate detection, validation rules, and role-based access controls that cover the bulk of governance needs without extra software. Beyond the CRM itself, teams typically add a data catalog or master data management layer for cross-system consistency, plus dashboard tooling like Sales-phoenix's executive dashboards to make quality metrics visible to leadership.
What Are the Four Pillars of a CRM?
The four functional pillars of a CRM are contact and account management, sales pipeline tracking, marketing and communication history, and customer service or support records. Governance sits underneath all four, since none of them stay reliable without consistent data standards and ownership.
What Is CRM in Data Management?
Within data management, a CRM functions as the system of record for customer, contact, and deal data that other tools and reports pull from. Its accuracy directly determines the reliability of forecasts, segmentation, and executive reporting built on top of it.
What Are the Five Pillars of Data Governance?
Common frameworks describe five pillars: data quality, stewardship, security, compliance, and lifecycle management, though exact definitions vary by source. In a CRM context, these translate to duplicate and fill-rate targets, assigned stewards, access controls, DSAR readiness, and a defined path from data entry through archival or deletion.